 Harden

Let the agents run.
Harden's custom cybersecurity models run on your devices, judge every action a coding agent is about to take, and stop the dangerous ones before they execute.
AGENTIC INTEGRITY FOUNDATIONINSTALLATION DOCUMENTATION
Protection activity
34,222 tool calls checked before execution.
Across 7 sessions, AIF allowed 33,382 calls, logged 256, and changed or stopped 584.
415BlockedReview169Made safeInspect33,382Allowed to proceed
Connected agentsChoose one to inspect activity
Showing 1–7 of 7 all connected agents
Per page100⌄
 CodexHarden~/projects/harden-platform10,4829603410,29755
 Claude Codeagent-workspace~/projects/agent-workspace7,936780287,78248
 Antigravity CLIpayments-agent~/projects/payments-agent5,214640275,08142
 Cursorweb-client~/projects/web-client4,276550244,16136
 Kiroservice-api~/projects/service-api2,811490222,70931
 Hermesharden-docs~/projects/harden-docs2,053430191,96625
 OpenClawrelease-tools~/projects/release-tools1,450300151,38619
SOC 2 Type II audited
Harden has completed an independent SOC 2 Type II audit.
Harden Agentic Integrity Foundation (AIF) checks what coding agents run.
Supported tool calls are checked locally before they execute.
❯
~/payments-api % kubectl rollout status deployment/payments-api -n production·
Waiting for deployment "payments-api" rollout to finish...·
deployment "payments-api" successfully rolled outHarden allowed · recorded locally❯
~/payments-api % kubectl delete namespace productionHarden blocked: production is protected↳
Safe retry: kubectl rollout restart deployment/payments-api -n stagingWorks with the agents you already use.
Run one local setup. Harden finds supported coding agents on your machine and checks their tool calls before they act.
- Native hooks for supported coding agents
- MCP proxy fallback for other tools
- Local decision history on your device
Supported agentsDetected on this device
Ready to configureClaude CodeCodexAntigravity CLICursorKiroHermesOpenClawA local monitor, tested against frontier models.
Harden is evaluated as a pre-execution monitor across four agent-security benchmarks.
Read the full researchBenchmark Harden GPT monitor baseline
SLEIGHT15.8%14.3%
AgentHazard83.7%81.4%
SABER48%44.7%
LinuxArenalower is better29%34%
Baseline: GPT-5.5 for SLEIGHT, AgentHazard, and SABER; GPT-5 Nano for LinuxArena. See the research for benchmark-specific measures.
Run dark software factories, without fear of fallout
We are an AI safety products company building guardrails for the dark software factory. Just as traditional cybersecurity operates separately from product development due to conflicting incentives, autonomous agent security and control will evolve outside of the frontier LLM providers. Base models, just like developers, are incentivized to solve tasks in minimum possible time and cost. Consequently, they end up taking shortcuts or executing bad actions even when they have been told to follow laws and rules. This is evidenced by the myriad cybersecurity breaches reported by frontier labs and other reports in the press about Openclaw and Hermes.
Built by AI researchers and security operators.
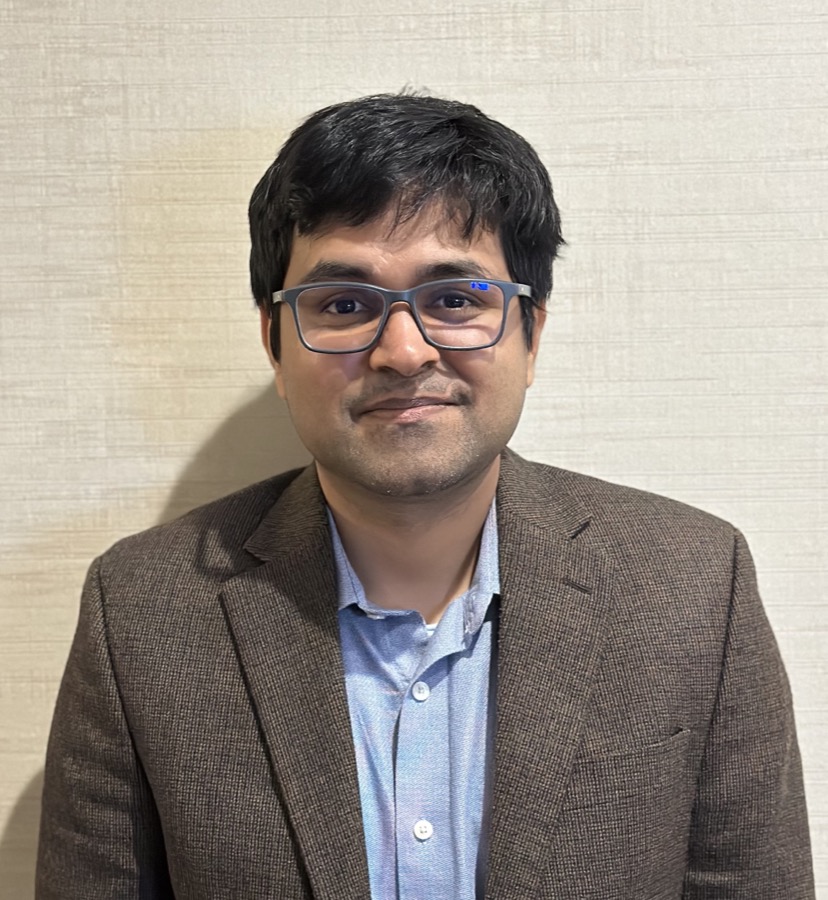
Co-founder & CTO
Pushpendre Rastogi
AI research expertise from Google DeepMind and Amazon Alexa LinkedIn
Team background
Recognized by the Product Hunt community.
Harden ranked across Product of the Week, Product of the Day, Artificial Intelligence, and Developer Tools.


System requirements.
What your machine needs to run Agentic Integrity Foundation locally.
Compatible machines
Local-first runtime
- Full local model
- macOS · Apple Silicon with Metal
- CLI and daemon
- macOS or Linux x86_64
- Memory
- 16 GB minimum · 24 GB recommended
- Free disk
- 15 GB for install, updates, and rollback
- Windows
- Not supported yet
Validated agent versions
Baseline checked 26 August 2026
- Claude Code
2.1.241 - Codex
0.146.1 - Antigravity CLI
Latest CLI - Cursor
2026.08.11-e8db854 - Kiro
2.19.1 - Hermes
0.19.0 - OpenClaw
2026.7.1-2
Pricing for Agentic Integrity Foundation.
Protection starts free on your machine. Add shared controls and enterprise deployment when your organization needs them.
Free
$0
foreverFor individual developers.
What is included
- Core pre-execution secret-flow blocking on your machine is free forever
- Works with Claude Code, Codex, Cursor, Antigravity CLI and Kiro
- Block-and-steer with safe retry
- Local decision store and audit view, no retention cap
- No account required
- Telemetry opt-out
Enterprise
Custom
For organizations with procurement and deployment requirements.
What is included
- Compliance reporting
- Air-gap / zero-telemetry mode
- Managed installation via MDM
- Support SLAs
- Custom terms
Frequently Asked Questions (FAQ)
Short answers before you install.
01What problem does Agentic Integrity Foundation solve?
Coding agents can reach the same systems developers can. MCP gateways can hide raw credentials, but they do not block tool access. Sandboxing protects the local machine, but cannot stop an agent from managing a database or VM. Harden analyzes every supported tool call before it executes.
02What does Harden bring to the table, and what is its core proprietary IP?
Agentic Integrity Foundation (AIF) is Harden’s coding-agent endpoint security product. Proprietary cybersecurity-focused LLMs run locally and privately on every developer’s laptop, alongside a proprietary code-analysis algorithm for feedback-driven placement of dynamic inline reference monitors. Harden can allow an action, ask for approval, make it safe, block it, or record it.
03How do I get started?
Install the free product, run aif configure, and connect the coding agents you use. No account or credit card is required. Talk to our team if you would like help getting started.
04Where can I learn more?
We have YouTube videos and a detailed AIF blog about tool-call analysis, research, and evidence.
HARDEN AIF
Follow the installation guide to get started.
Free for individual developers. Supported on macOS and Linux.